Blog
How-tos, research, and lessons on securing APIs, AI, and the modern application surface.
November 9, 2026
A coding agent gave an AI support bot the power to issue refunds. See how Surface Code AI caught it in the session and what runtime testing must prove.
7 min
November 4, 2026
Perry Menezes on using Claude in the AppSec program you already have: a five-step blueprint, exploitability over volume, and governing the AI agent.
October 28, 2026
Former Charles Schwab CISO Bashar Abouseido explains why AI-driven attacks demand hyper defense, and why exploitability, not patch speed, sets priorities.
March 25, 2026
How to detect and prevent NoSQL injection in APIs with MongoDB examples, operator payloads, and secure code fixes.
March 24, 2026
How to test and prevent SQL injection in APIs with code examples, WAF bypass techniques, and proven defense strategies.
March 23, 2026
SQL injection targets APIs through JSON bodies, query params, and headers. Get API-specific payloads, code fixes, and a testing checklist.
March 9, 2026
HTTP request smuggling lets attackers bypass API gateway security controls. See API-specific attack types, real CVEs, payloads, and prevention strategies.
Broken access control is the #1 API risk. See API-specific examples of BOLA and BFLA, testing methods, real breaches, and proven prevention strategies.
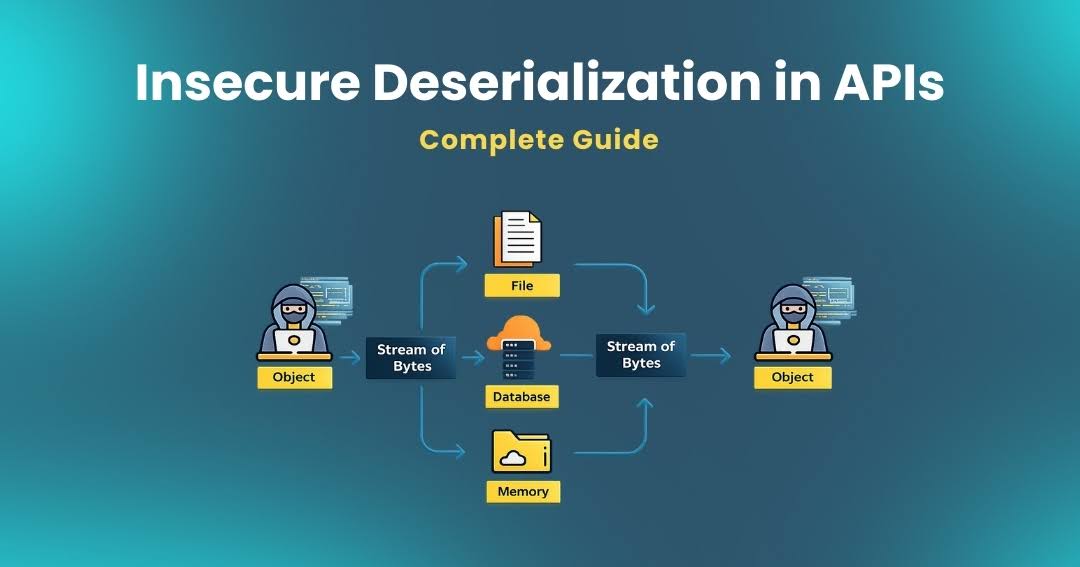
Insecure deserialization lets attackers execute code through API endpoints. See how deserialization attacks work, real CVEs, and proven prevention strategies.
March 4, 2026
Race condition vulnerabilities let attackers exploit timing gaps in API logic. See real attack patterns, code examples, and proven prevention strategies.
March 5, 2026
Path traversal attacks let hackers read sensitive server files through API endpoints. See API-specific examples, payloads, and prevention strategies.
February 9, 2026
Compare top API discovery tools that find shadow APIs, zombie endpoints, and hidden vulnerabilities across your environment.
Manual pentesting vs automated API security: compare which approach protects modern APIs. Analyze speed, coverage, and cost to secure your endpoints effectively.